Space Explorer (HackTheBox): bypassing access control with JSON parser differences
Challenge: Space Explorer on HackTheBox.
Scenario: A lost space mission control system suffers from flawed authentication logic between its Sender and Receiver services.
Analysis
The challenge runs two services: a Go application (main.go) and a Flask API (app.py).
main.go serves the HTML page and forwards commands to the Flask API with a POST request.
On the Python side, the /execute route reads the action field of the incoming JSON:
@app.route('/execute', methods=['POST'])
def execute():
    if not request.is_json:
        return jsonify({"error": "Invalid transmission format"}), 400

    data = request.get_json()

    if 'action' not in data:
        return jsonify({"error": "No command received"}), 400

    if data['action'] == "getcosmic":
        anomaly = random.choice(COSMIC_ANOMALIES)
        return jsonify(anomaly)
    elif data['action'] == "getSecureCode":
        return jsonify({
            "flag": os.getenv("FLAG", "HTB{flag_not_set}"),
            "name": "Captain's Log",
            "src": "https://images.unsplash.com/photo-1534447677768-be436bb09401?w=600"
        })
    else:
        return jsonify({"error": "Unknown command"}), 400
So the API has to receive the getSecureCode action to return the flag. It can’t be reached directly, because the Dockerfile doesn’t expose it: everything has to go through the Go application.
The catch is that the Go application answers “Access denied” as soon as the action is getSecureCode. Only the getcosmic action is forwarded to the API, with the request body passed through as is:
	case "getcosmic":
		resp, err := http.Post("http://localhost:8081/execute", "application/json", bytes.NewBuffer(body))
		if err != nil {
			log.Printf("Failed to reach cosmic scanner: %v", err)
			http.Error(w, "Scanner offline", http.StatusInternalServerError)
			return
		}
		defer resp.Body.Close()
		io.Copy(w, resp.Body)
	case "getSecureCode":
		w.Write([]byte("Access denied: Invalid security clearance"))
	default:
		http.Error(w, "Invalid command", http.StatusBadRequest)
	}
What we need is a request that:
- Go reads as
getcosmic, so it gets forwarded to the API; - Python reads as
getSecureCode, so it returns the flag.
Exploitation
The two JSON parsers don’t behave the same way:
- Go’s parser (
encoding/json) matches keys to struct fields case-insensitively, and when a key appears more than once, the last one wins; - Python’s parser is case-sensitive:
actionandActionare two different keys.
So, with Burp Suite, we send:
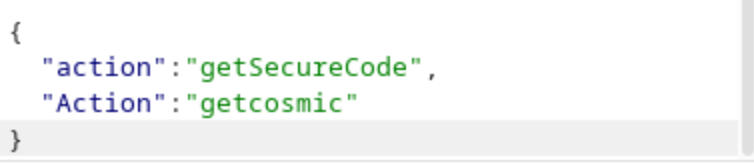
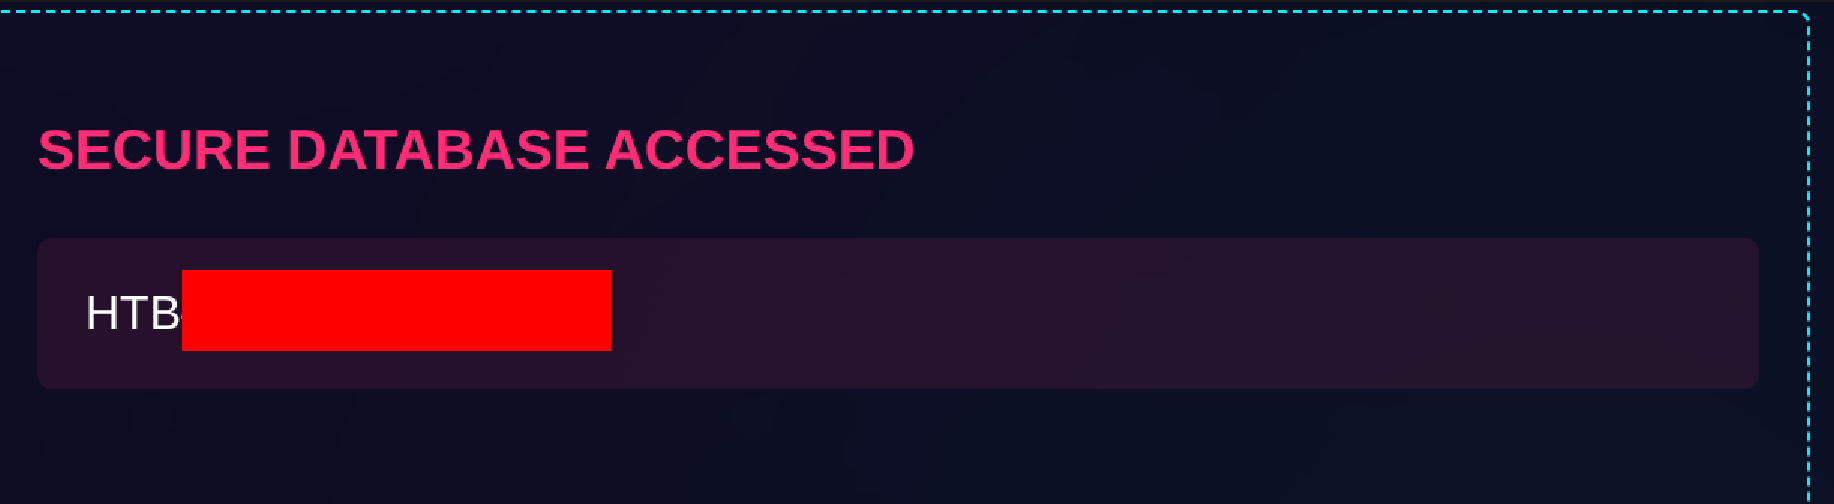
Go sees two keys matching its action field, keeps the last one ("Action": "getcosmic") and forwards the request. Python only reads the exact action key and runs getSecureCode:
Takeaway
When two services parse the same message, they must interpret it the same way. Here, access control is enforced by one service and the action is carried out by another, so a divergence between their parsers is enough to bypass the check. The fix is to forward a request rebuilt from what Go validated, rather than the raw body it received.